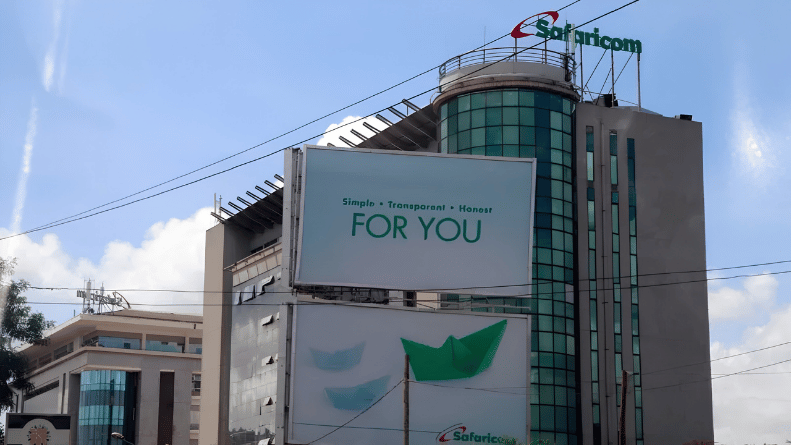

Safaricom Group has revealed that its servers repelled a staggering 1.25 billion cyber intrusion attempts over a single financial year.
The telecommunications giant unveiled these figures in its latest 2026 Sustainable Business Report, shedding light on the escalating scale of digital threats targeting Kenya’s critical national infrastructure.
The disclosure highlights a dramatic intensification of global and local cyber security challenges as financial systems and consumer services become increasingly digitized.
While the total volume of attacks averages out to over 3 million daily intrusion attempts, Safaricom confirmed that its defensive frameworks successfully prevented widespread service disruption across its network.
The surge comes as telecommunications operators and financial institutions across Africa face sophisticated threats ranging from automated botnet probes to targeted credential-harvesting operations.
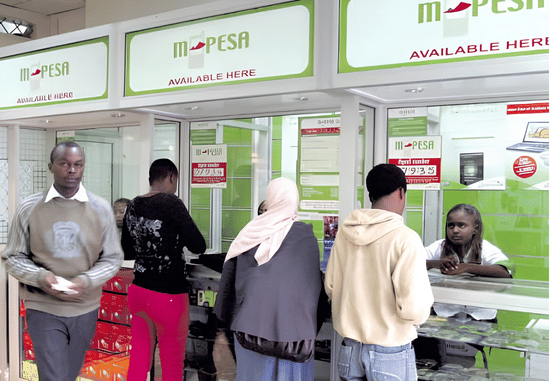
As digital finance platforms scale to support millions of daily transactions, network operators must continuously balance service accessibility with rigorous data protection standards.
Also Read
OpenAI Introduces Ads to Free ChatGPT Plans
5 USSD Codes All Kenyans Must Know, Including the One to Join Sifuna’s New Party
Top 5 Websites for Kenyans to Find Remote Jobs Paying in Dollars
How is Safaricom Safeguarding M-PESA and Customer Data
To address public concerns regarding financial safety, Safaricom noted that its dedicated security operations center actively deep-investigated over 130,000 high-priority security events during the period.
The company reaffirmed that core customer databases and primary M-PESA transaction ledgers remained secure despite the persistent volume of network probes hitting outer perimeter firewalls.
Data privacy and user protection remain central to the telco’s operational strategy, with automated threat-detection systems deployed to neutralize malicious traffic before it reaches user-facing applications.
Beyond external attacks, Safaricom has also sharpened its internal risk controls, using advanced data analytics to identify internal compliance breaches and audit transaction irregularities.
The telco emphasized that safeguarding subscriber identities, personal call records, and digital wallets requires continuous investments in artificial intelligence and machine learning threat monitoring.
Users are encouraged to maintain strict personal security hygiene, such as enabling multi-factor authentication and avoiding unverified links, to help protect their personal accounts from phishing attempts.